
Consulting
Consulting on IT-Grundschutz and Grundschutz++
Blackfort Technology supports organisations in moving to Grundschutz++ under BSI Standard 300-1 of the German Federal Office for Information Security (Bundesamt für Sicherheit in der Informationstechnik, BSI), in building or migrating an ISMS under IT-Grundschutz, the BSI's methodology for information security management, and in preparing for the audit. Consulting is delivered by a team. Scope and price are set in a binding offer after a free initial call.
When consulting makes sense
With version 1.0 of 20 October 2026, the Grundschutz++ method is available as BSI Standard 300-1. From 1 January 2027, according to the BSI milestone plan (Meilensteinplan), ISO 27001 certification based on Grundschutz++ can be applied for; classic IT-Grundschutz remains certifiable until 30 November 2031. Organisations that already work with IT-Grundschutz or have to show it therefore face a decision: continue, switch or start from scratch, and when.
The standard requires several changes that cannot be handled alongside day-to-day work: protection requirements (Schutzbedarf) per business process in two categories, modelling via target object categories (Zielobjektkategorien), an implementation status (Umsetzungsstatus) without "partially", MUST requirements without exception and a risk method meeting 35 minimum criteria (Mindestkriterien). The BSI mapping from the IT-Grundschutz Compendium (IT-Grundschutz-Kompendium), edition 2023, to Grundschutz++ is still a draft, and the user catalogue (Anwenderkatalog) as of 29 October 2026 deviates from the standard in individual points.
Typical reasons to get in touch: an international IT service provider whose German public-sector client expects Grundschutz evidence; a group headquarters abroad whose German entity holds an ISO 27001 certificate based on IT-Grundschutz with recertification coming up; an organisation building an ISMS for its German operations that wants to start directly with 300-1.
Five packages
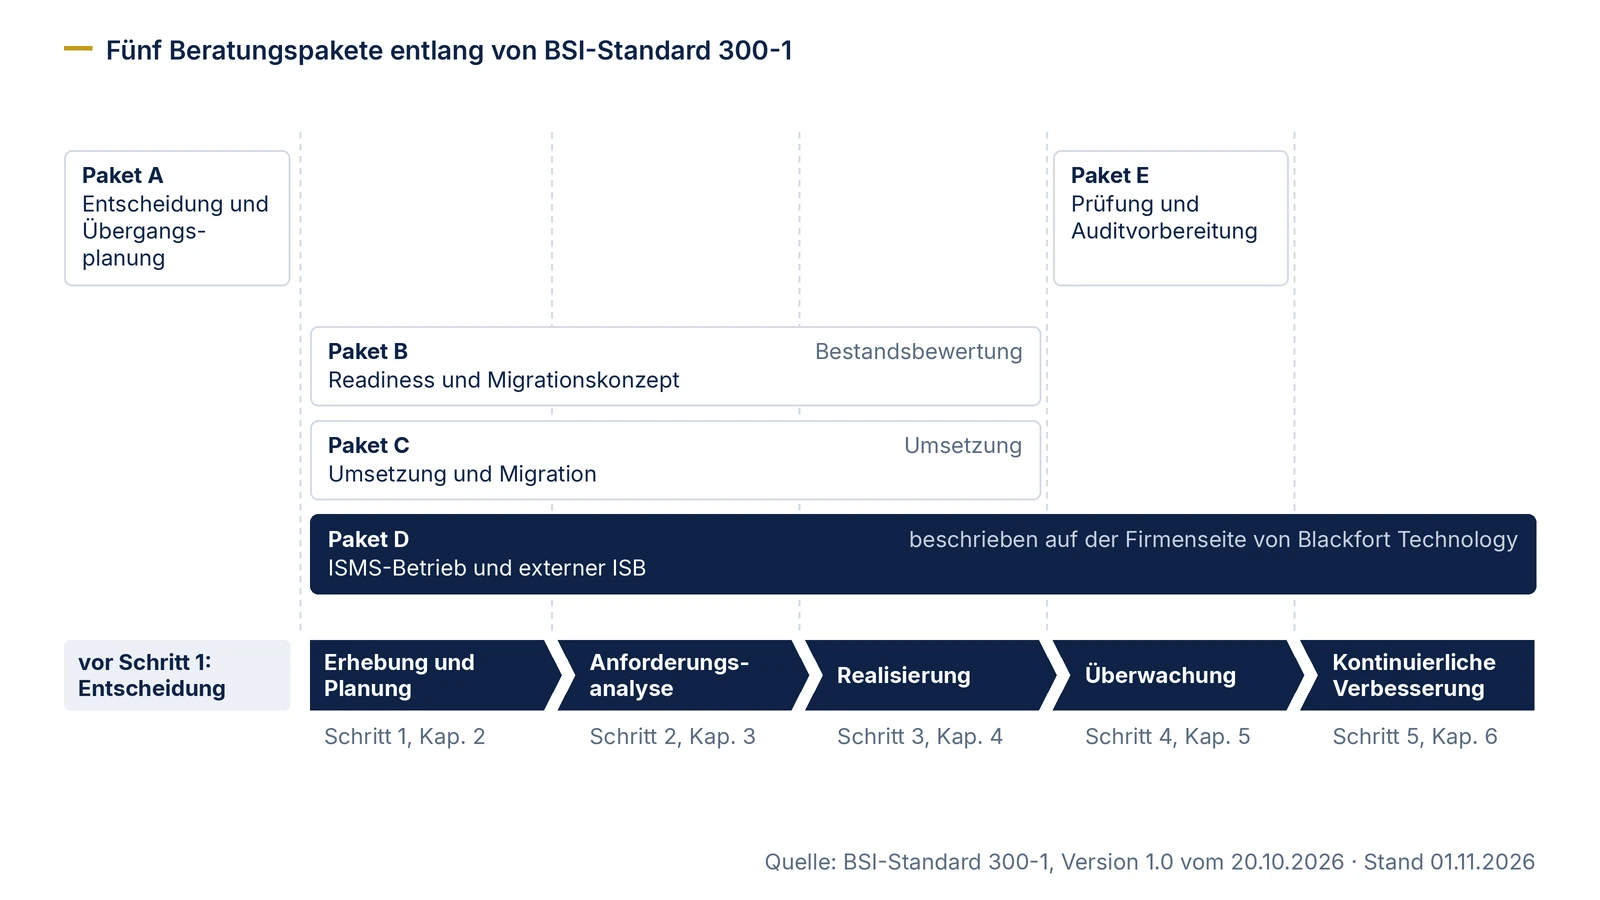
The packages follow the process steps of BSI Standard 300-1, so you can see which part of the method is done after each package. They can be commissioned individually or one after the other.
Package A
Decision and transition planning
Decision paper for top management: classic IT-Grundschutz, ISO 27001 without a Grundschutz basis or Grundschutz++, and from when, with a view to your recertification dates up to 2031. We assess the requirements and client demands you name, or that appear in your documents, from an information security perspective; whether and how they legally apply to you is for your legal department to assess.
ISO 27001 vs. IT-GrundschutzPackage B
Readiness and migration concept
Assessment of an ISMS under the Compendium 2023 or ISO 27001 against 300-1: method delta, comparison using the BSI mapping tables, check of the risk method against the 35 minimum criteria, migration plan with order and responsibilities.
IT-Grundschutz vs. Grundschutz++Package C
Implementation and migration
New build under 300-1 from the first business process, or transfer of an existing ISMS under the Compendium 2023 or ISO 27001: business processes and protection requirements, requirements package (Anforderungspaket), implementation status, risk method under Annex 3, implementation and evidence plan. Together with you we define in the evidence plan which evidence can come from tools already running in your operation.
Grundschutz++ migrationPackage D
ISMS operation and external information security officer
Ongoing operation of the ISMS with progress tracking, risk review and management reports, on request with the role of external information security officer (externer Informationssicherheitsbeauftragter, ISB). Blackfort Technology describes this service on its company website.
Blackfort Technology websitePackage E
Review and audit preparation
Internal audits under chapter 5.2 of 300-1, review of the documents before the certification audit, support during the audit and handling of nonconformities. We do not carry out internal audits of an ISMS that we helped to build.
What you will have in hand
Each package ends with documents you can maintain yourself. They refer to the text of 300-1, with chapter references.
01
Decision paper
Framework, timing, resource needs and open points on a few pages, as a submission to top management under chapter 2.10.
02
Delta list and migration plan
What stays, what changes and what is added, with effort level and order.
03
Requirements package and implementation plan
Package with defined parameters, status per requirement, measures with owner and deadline.
04
Evidence plan
Assignment of requirement, measure and evidence with supplying and checking role and date under chapter 4.3.
05
Risk method with criteria evidence
Procedure, roles, criteria and register, with one line per minimum criterion of Annex 3.
06
Audit report and list of findings
Result of the internal audit or the document review before the certification audit, with findings and recommendations.
Which package fits your starting point
The table is for orientation. We settle the exact scope in the initial call.
| Starting point | Typical question | Entry | Next |
|---|---|---|---|
| No ISMS, client expects Grundschutz evidence | Where do we start and how big is the first step? | Package A | Package C from the first business process |
| ISMS under the Compendium 2023 with certificate | When do we switch and what changes for us? | Package B | Package C at the next recertification, then package E |
| ISMS under ISO 27001 without a Grundschutz basis | How much of Grundschutz++ do we already cover? | Package A or B | Package C |
| ISMS under Grundschutz++ being built, audit planned | Are we ready for the audit? | Package E | - |
| ISMS in place, information security officer role vacant | Who runs the ISMS day to day? | Package D (company website) | - |
Orientation without guarantee for the individual case. The legal classification of your obligations is for your legal department.
How we work
From the first enquiry to acceptance in four steps.
1
Initial call
Free and without obligation: starting point, goal, dates. Afterwards you know which package fits.
2
Scoping and offer
We review existing documents and define the scope, such as the number of business processes, sites, operating models and main service providers. You receive a binding offer.
3
Delivery
Work in workshops and on the material, with fixed sign-off points and a named contact on your side.
4
Acceptance and handover
Results meeting, correction round, acceptance. Your internal coordinator can then maintain the documents.
Your contact
Christian Gebhardt · Founder and managing director, Blackfort Technology
Christian Gebhardt, founder and managing director of Blackfort Technology, is happy to take your enquiry personally. In a free initial call you work out together what you need; the consulting is carried out by the Blackfort Technology team.
Experience
The Blackfort Technology team has project experience in building an ISMS under BSI Standards 200-1, 200-2 and 200-3 up to initial certification, including support through the audit, and in the role of external information security officer. We do not name clients.
On Grundschutz++ we work from the text of the standard and the BSI catalogue data: we count the user catalogue ourselves (most recently the build of 29 October 2026), check statements against the wording of 300-1 and document where catalogue and standard still diverge. The subject pages of this website, most of them in German, show how we go about it.
What we need from you
A contact person
An internal coordinator who arranges dates, provides documents and continues the results afterwards.
Existing documents
Information security policy (Leitlinie), structure analysis (Strukturanalyse) or asset data, protection requirements assessment (Schutzbedarfsfeststellung), modelling, results of the IT-Grundschutz Check, risk analyses, where applicable an export from your ISMS tool.
Business units
The owners of the business processes, because under 300-1 protection requirements are set per business process.
IT operations
Access to reports and configuration states from which technical evidence is produced.
Top management
Dates for decisions and approvals. Under 300-1, responsibility for the ISMS lies with top management (Institutionsleitung) and cannot be delegated.
What is not included
So that it is clear what you can expect:
- No legal advice. Whether and how requirements legally apply to you is for your legal department to assess (we provide no legal services within the meaning of the German Legal Services Act, RDG).
- No certification audit. Whoever advises does not audit the same organisation; the audit is carried out by an independent auditor.
- No internal audits of an ISMS that we helped to build.
- Technical implementation in your systems lies with your IT operations or your service providers; we plan, check and document.
- No training courses for the BSI personal certifications as IT-Grundschutz practitioner (Praktiker) or consultant (Berater).
- ISMS consulting under ISO 27001 without a Grundschutz basis, NIS2 implementation and BSI C5 are offered by Blackfort Technology on its company website (link under "Further reading").
We do not publish prices on this website. After the initial call you receive a binding offer for the agreed scope.
Frequently asked questions
What does Grundschutz consulting cost?
That depends on the scope, for example the number of business processes, sites and operating models, the main service providers and the quality of the existing documentation. After the free initial call you receive a binding offer.
Do you also advise on classic IT-Grundschutz under BSI Standard 200-2?
Yes. According to the BSI milestone plan, classic IT-Grundschutz remains certifiable until 30 November 2031. We support existing ISMS under 200-2 and plan with you whether and when a switch to Grundschutz++ makes sense.
Do you also carry out the certification audit?
No. Whoever advises an organisation does not audit it. We prepare the documents, review them before the audit on request and support you during the audit; the certification audit itself is carried out by an independent auditor.
Can you also provide the external information security officer?
Yes, as package D. Blackfort Technology describes this service on its company website, https://www.blackfort-tec.de/en.
Further reading
Get in touch
Initial call about your Grundschutz project
Briefly describe your starting point: existing ISMS, certificate, dates. In the free initial call we work out which package fits.
Request an initial callSources
- BSI Standard 300-1 „Methodik Grundschutz++“, version 1.0 (German) (version 2026-10-20), retrieved 2026-11-01
- BSI: Grundschutz++ topic page with milestone plan, as of October 2026 (German), retrieved 2026-11-01
- BSI State-of-the-Art Library (Stand-der-Technik-Bibliothek), Grundschutz++ user catalogue (build 2026-10-29) and mapping IT-Grundschutz 2023 to Grundschutz++ (status draft) (version 2026-10-29), retrieved 2026-11-01
Quotations from BSI standards and BSI web pages are © Federal Office for Information Security (BSI) and are reproduced verbatim, in quotation marks and with source reference. This is an independent offering, not an offering of the BSI.
- Last updated
- 2026-11-02
- Technically reviewed
- 2026-11-02
This content provides general technical and organisational information on IT-Grundschutz and Grundschutz++ and does not constitute legal advice (no legal services within the meaning of the German RDG). It replaces neither an audit nor a decision by the certification body.