
The short answer
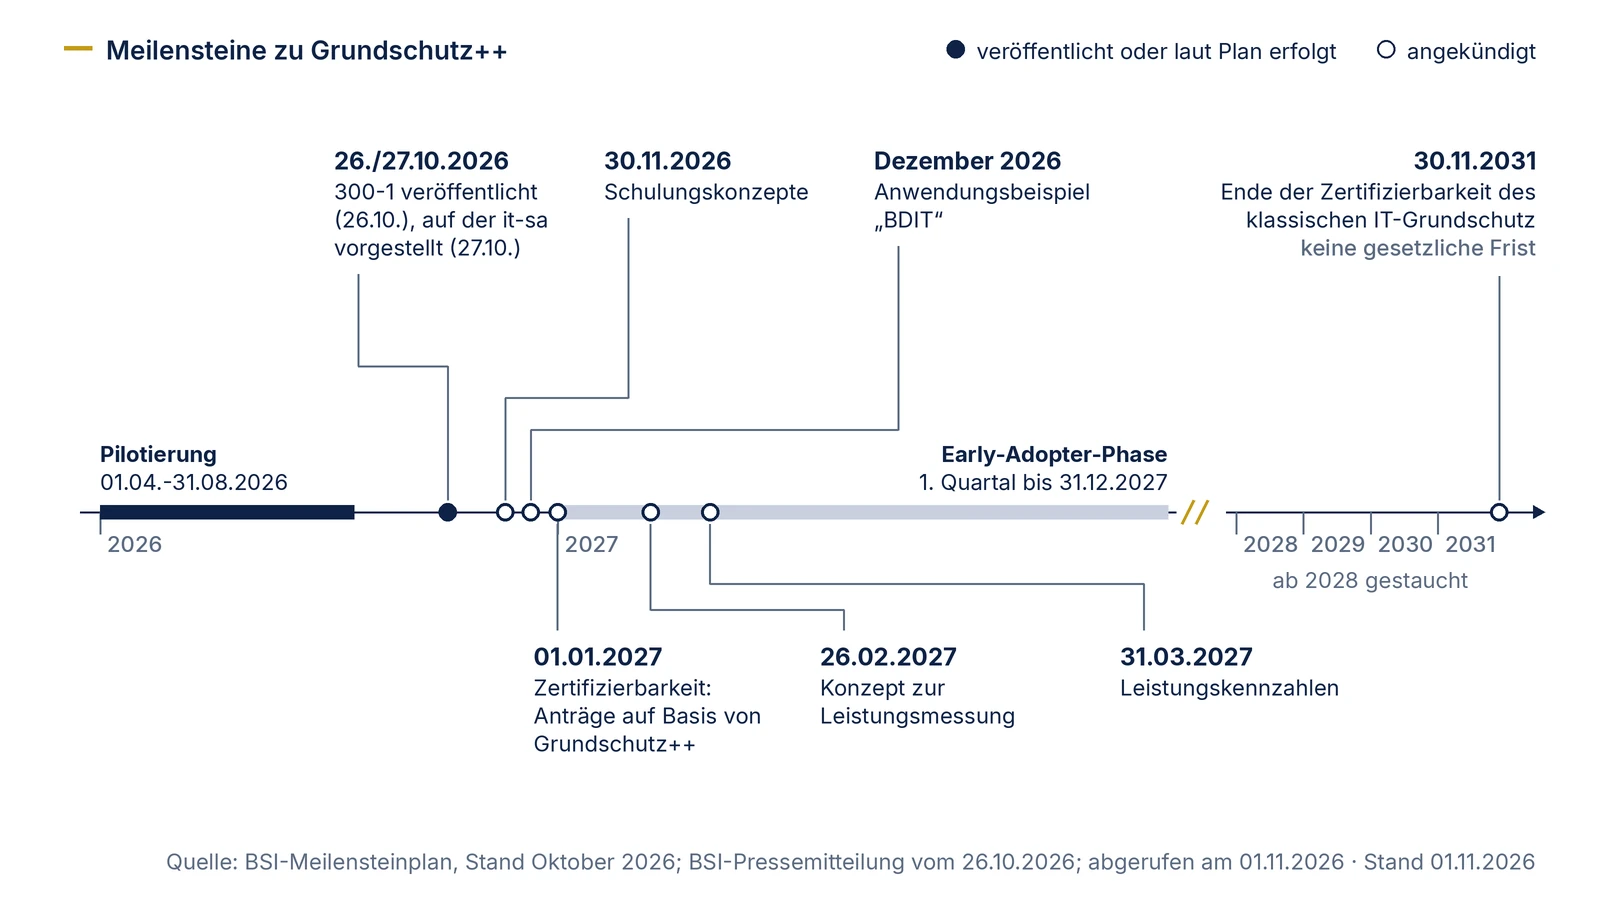
Three dates determine most plans. Version 1.0 of 300-1 is dated 20 October 2026 and, according to its change history, is the „Initiale Veröffentlichung der ersten anwendbaren Version“ (our translation: "initial publication of the first applicable version"); the BSI published it on 26 October 2026 according to its press release. From 1 January 2027, according to the milestone plan (Meilensteinplan), applications for ISO 27001 certification based on Grundschutz++ can be submitted, as can applications for certification as GS++ consultant (GS++-Berater) and GS++ audit team leader (GS++-Auditteamleiter). On 30 November 2031 certifiability of classic IT-Grundschutz ends, five years after the publication of Grundschutz++ according to the BSI.
In between, further parts are delivered: training concepts, a worked example, the concept for performance measurement and indicators. The BSI itself points out that the milestone plan is „stetig angepasst“ (our translation: "continuously adjusted"). All information on this page reflects the milestone plan as of October 2026, retrieved on 1 November 2026.
Grundschutz++ date register
Status: published means the document or event exists; version date means the date is stated in the document itself; done according to plan means the date is in the past and appears in the milestone plan without our having checked it separately; announced means the BSI plans it; statutory means the date is in the law. The column "consequence" is our professional assessment.
| Date | Event | Status (1 Nov 2026) | Source | Consequence for your planning |
|---|---|---|---|---|
| 1 Jan 2026 | Deadline for the BSI to modernise and further develop IT-Grundschutz | statutory | Section 44(1) sentence 6 of the BSI Act (BSIG) | For the federal administration the question remains which version applies; the BSI publishes it on its website under Section 44(1) sentence 3 BSIG. |
| 1 Apr to 31 Aug 2026 | Pilot phase with partners from public administration and the private sector | done according to plan | BSI milestone plan | No consequence of its own; explains why 300-1 has already been trialled. |
| 21 Jul 2026 | Version date of the mapping table IT-Grundschutz 2023 to Grundschutz++ | published, status "draft" | State-of-the-Art Library (Stand-der-Technik-Bibliothek) | Usable for a first comparison; check every mapping as a draft. |
| 20 Oct 2026 | Date of version 1.0 of BSI Standard 300-1 „Methodik Grundschutz++“ | version date | 300-1, change history | Use the version date 20 October 2026 for references. |
| 26 Oct 2026 | Publication of BSI Standard 300-1 (version 1.0) | published | BSI press release of 26 Oct 2026 | From here you can work under Grundschutz++. The version is aimed primarily at „Early Adopters“. |
| 27 Oct 2026 | Presentation of 300-1 at it-sa in Nuremberg | done according to plan | BSI milestone plan | No consequence of its own. |
| 29 Oct 2026 | Current build of the Grundschutz++ user catalogue (Anwenderkatalog) | published, rebuilt continuously | State-of-the-Art Library | Fix the catalogue version for your own work and record date and commit. |
| 30 Nov 2026 | Training concepts for GS++ practitioners (GS++-Praktiker) and GS++ consultants | announced | BSI milestone plan | Plan your team's training only after this. |
| Dec 2026 | Worked example based on the fictitious model authority „BDIT“ | announced | BSI milestone plan | Check your own templates against the example afterwards. |
| 1 Jan 2027 | Grundschutz++ certifiable: applications for ISO 27001 based on Grundschutz++ and for GS++ consultants and GS++ audit team leaders | announced | BSI milestone plan | Earliest application date for a certificate based on Grundschutz++. |
| Q1 2027 | Separate further training for already certified IT-Grundschutz consultants and audit team leaders to become GS++ consultants and GS++ audit team leaders | announced | BSI milestone plan | If you plan an audit under Grundschutz++, clarify early when audit team leaders with GS++ certification will be available; this cannot be said today. |
| Q1 to 31 Dec 2027 | Early adopter phase for applying 300-1 | announced | BSI milestone plan | Early users gather experience that, according to 300-1, feeds into further development; expect changes to the standard. Whether and when a revised version follows is not stated in the plan. |
| 26 Feb 2027 | Concept for measuring ISMS performance integrated into the method | announced | BSI milestone plan; 300-1 ch. 5.1 | Until then organisations are free to design their performance evaluation; mark your own definitions as such. |
| 31 Mar 2027 | Performance indicators for every requirement of the methodology practices | announced | BSI milestone plan | Adjust management report and indicator system afterwards. |
| 2027 onwards | Internationalisation of Grundschutz++, integration of other management systems | announced, no date | BSI milestone plan | No basis for planning; keep an eye on it. |
| 30 Nov 2031 | End of certifiability of classic IT-Grundschutz | announced | BSI milestone plan | After this date classic IT-Grundschutz is no longer certifiable according to the BSI. Not a statutory deadline. |
What the dates mean
Applicable and certifiable are two different things. Since October 2026 an organisation can build and run its ISMS under 300-1. A certificate under ISO 27001 based on Grundschutz++ can only be applied for from 1 January 2027 according to the milestone plan. Anyone starting now is working towards a date on which the scheme only begins; audit experience under Grundschutz++ cannot exist before then.
The early adopter phase runs from the first quarter to 31 December 2027 according to the plan. The standard names experienced organisations that want to implement early as the main audience of version 1.0 and announces that their experience will feed into further development. Standard and catalogue may therefore still change during this period. The user catalogue is already rebuilt continuously; in the build of 29 October 2026 it is not yet aligned with 300-1 in some points.
Two dates fill gaps in the standard. Chapter 5.1 of 300-1 states expressly that uniform requirements for performance evaluation are still pending and that organisations are free to design it until then. Anyone setting up an indicator system before February and March 2027 should expect to adjust it.
30 November 2031 is a BSI date for its own certification scheme. It marks the last date on which classic IT-Grundschutz can be certified. It is not a statutory deadline and obliges no one to switch earlier. Whether an organisation has to switch earlier for other reasons, such as a contract, is a separate question.
What the milestone plan does not cover
- Existing certificates: how certificates under ISO 27001 based on IT-Grundschutz issued before 30 November 2031 are treated, for example in surveillance audits after that date, is not in the milestone plan. Ask your certification body or the BSI before you base your planning on it.
- BSI Standards 200-1 to 200-3: neither the milestone plan nor 300-1 says whether and when they will be formally withdrawn. BSI Standard 200-4 on business continuity management is not replaced by 300-1. What the integration of other management systems announced for 2027 onwards means for 200-4 is not stated in the plan.
- Federal administration: Section 44(1) BSIG requires bodies of the federal administration to meet minimum requirements that follow from the BSI standards, the IT-Grundschutz Compendium (Grundschutzkompendium) and the federal minimum standards (Mindeststandards des Bundes) „in den jeweils geltenden Fassungen“ (our translation: "in the versions applicable at the time"), which the BSI publishes on its website. Neither the Grundschutz++ topic page nor 300-1 states expressly from when Grundschutz++ applies in this sense. The user catalogue names „§ 44 Abs. 1 BSIG“ in its metadata as the implemented provision, but gives no date from which it applies as the version in force. Section 43(1) BSIG also requires bodies of the federal administration to demonstrate to the BSI that they meet the requirements no later than five years after the Act entered into force, and regularly thereafter in line with its requirements. The legal assessment for your body is a matter for its legal department.
- Companies under Section 30 BSIG: for essential entities (besonders wichtige Einrichtungen) and important entities (wichtige Einrichtungen), Section 30 BSIG does not prescribe a framework. The dates in the milestone plan only concern them if they choose a Grundschutz certificate.
- Blueprints: 300-1 provides that mandatory blueprints may exist for certain organisations. When which ones will be published is not scheduled.
Building the dates into your own plan
- Set the target date. A certificate based on Grundschutz++ can be applied for no earlier than 1 January 2027. With an existing Grundschutz certificate, the right moment depends on your own audit and recertification dates.
- Obtain a management decision. 300-1 places approval of scope, protection requirements, order of business processes, resources and policy with top management (Institutionsleitung) (ch. 2.10). The target date belongs in the same decision paper.
- Freeze the catalogue version. Fix and document one build of the user catalogue for creating the requirements package (Anforderungspaket). Incorporate later builds when validating the requirements (ch. 5.5).
- Set checkpoints. Review the training concepts after 30 November 2026, compare the worked example with your templates after December 2026, adjust performance evaluation and indicators after February and March 2027.
- Watch the milestone plan. Decide who checks it at what interval and how changes enter your plan.
What the standard requires is on BSI Standard 300-1, the work packages of a switch on Grundschutz++ migration, and the choice between ISO 27001 and Grundschutz on ISO 27001 vs. IT-Grundschutz.